Encrypt SMS secrets
The twin of the Checkbox service, for SMS provider passwords: TurboSMS and Atompark.
Where to find it: Modules → Telephony → Maintenances → Encrypt SMS secrets
A worked example
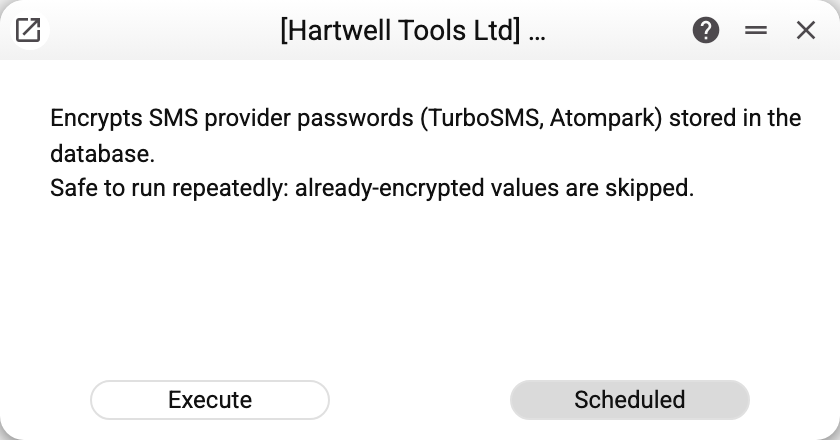
An explanation and one button again: the operation runs once, so scheduling is disabled.
What gets encrypted
The password from "Turbo SMS Settings" and the Atompark password — precisely the values that used to sit in the database in clear text. Already-encrypted and blank values are skipped, so a repeat run is safe.
Along the way, the search fingerprint of every record is rebuilt — without the password. This happens even when the password itself is already encrypted: the clear text could have stayed in the fingerprint from a save made before the field became write-only.
One detail matters: the service walks every company in the database at once, not just the current one. That is deliberate — a secret forgotten in another company would otherwise stay exposed.
If someone saved the settings while the service was running, the service leaves that record alone so as not to overwrite the password just entered, and says so in a summary line with a warning triangle. Run the operation again — it will finish that record.
Encryption key and failures
- The encryption key is part of the server configuration; it is not in the database. If the key is changed or lost, or the database is moved to a server with a different key, the stored passwords can no longer be decrypted, SMS stop going out, and the passwords have to be entered in the settings again.
- No key on the server — the service stops at the first plain-text password with the message "The secret could not be encrypted on the server. Ask the administrator to check the encryption key"; plain-text values stay as they were.
- There is no reverse operation, and records are written one by one, not in a single transaction: if the service stops halfway, what is done stays done, and a repeat run finishes the rest.
How to tell it worked
After the run the service shows a summary on screen: how many rows were encrypted, in how many an open password was found in the search text and removed, and in how many the search text was rebuilt without private fields.
Open "Turbo SMS Settings": a set password is shown as a mask of eight dots both before and after the run — the window shows no difference, and the password itself is never handed to the interface. Sending keeps working exactly as before — the system reads the stored value itself, as long as the server's encryption key stays the same.
Where to look next
- Turbo SMS Settings — where the password lives.
- Encrypt Checkbox secrets — the same for the fiscal service.